Convenience that becomes a liability
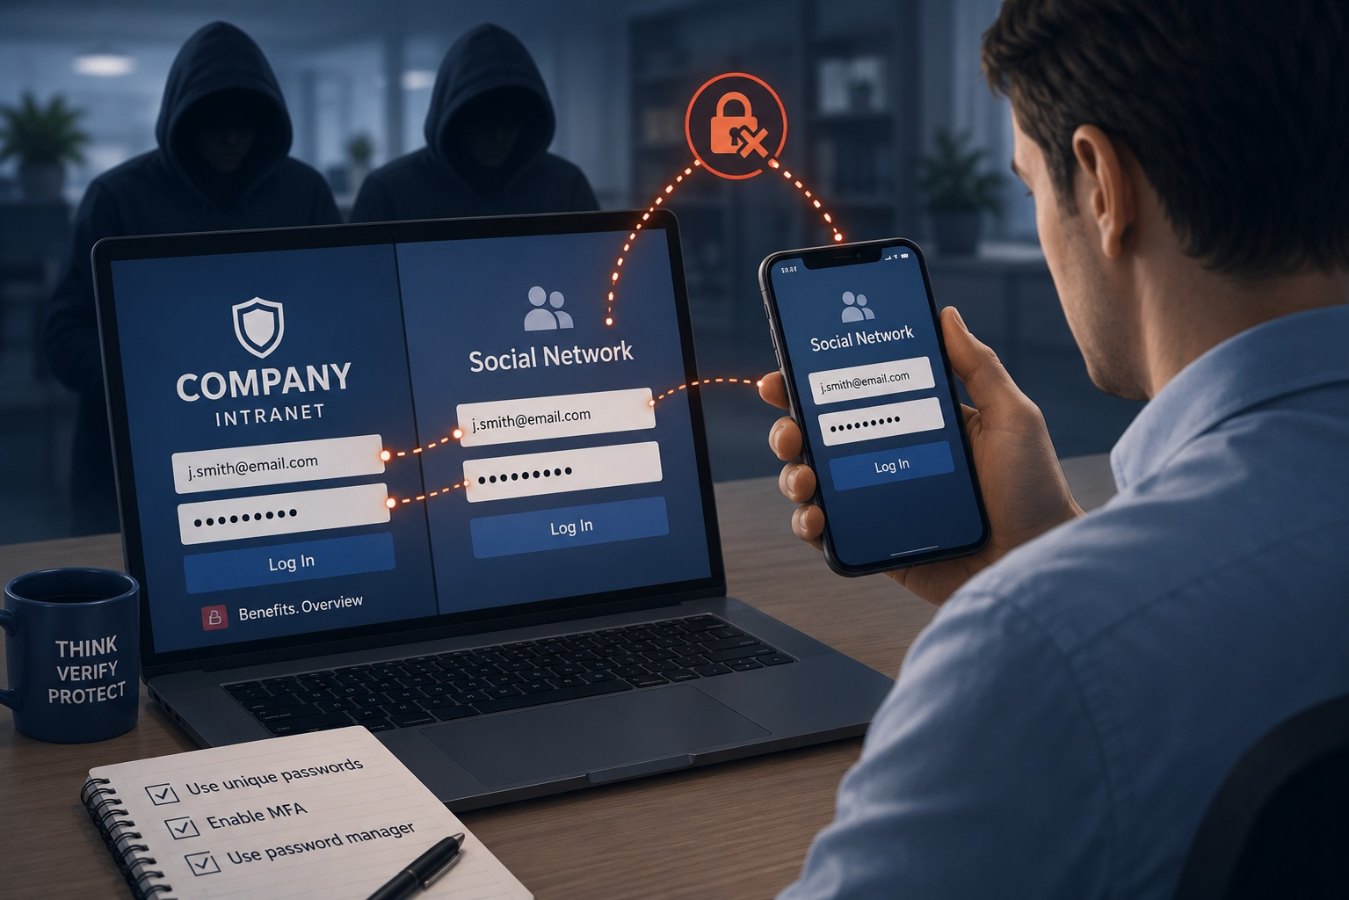
Most people juggle dozens of logins. It’s tempting to use the same or similar password on multiple websites so there’s less to remember. Unfortunately, credential‑stuffing attacks make that habit dangerous. When one service is breached and passwords are dumped online, criminals use automated tools to test those username/password pairs on other sites. If you’ve reused credentials, your accounts at work could be compromised without anyone noticing until damage is done.
How credential stuffing works
Attackers harvest huge lists of stolen login details from dark‑web markets or previous data leaks. Automated scripts then try those credentials against corporate VPNs, email portals and cloud services. Because many people reuse passwords, a small percentage of attempts succeed. Once inside, adversaries can move laterally, access sensitive data or plant malware. These intrusions often look like legitimate logins, making them harder to detect.
Real‑world impacts on teams
A single compromised account can be the doorway to an entire network. Attackers often target payroll systems, customer databases or proprietary documents once they gain a foothold. Remediation is expensive – from resetting passwords and investigating unauthorised activity to notifying affected customers. It also erodes trust within the organisation and can lead to regulatory penalties if personal data is exposed.
Best practices to stay protected
The most effective defence is simple: use a unique, strong password for every account. Password managers make this manageable by generating and storing complex credentials so you don’t have to remember them all. Enable multi‑factor authentication (MFA) wherever possible. MFA requires a second form of verification, such as a one‑time code or biometric, which prevents attackers from logging in even if they have your password.
For shared team accounts, implement single sign‑on solutions that enforce robust password policies and integrate with your MFA provider. Regularly review access logs to spot unusual patterns and rotate credentials if a third‑party service is breached. Educate colleagues about the risks of password reuse and provide tools that make secure behaviour easier.
Building a security‑first habit
Creating and maintaining unique passwords may seem tedious, but it’s a fundamental part of protecting your organisation. Encourage employees to use trusted password managers and avoid storing credentials in plain text. Reinforce the importance of MFA during onboarding and in refresher training. By making secure practices the path of least resistance, you reduce the likelihood that convenience will override caution.